






http 流包装器是 php 里最常用的功能之一——file_get_contents 和各种 http:// 流都走这条路径。ghsa-fpwc-w8rq-cr92 公告披露:当请求跟随外部重定向时,会发生跨源凭据泄漏,评级 moderate。
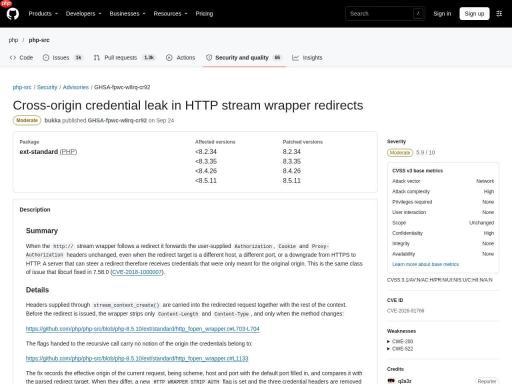
▲ 事件来源页面实时截图:php/php-src Security Advisories
攻击场景
你的代码请求域 A,域 A 重定向到域 B,某些凭据(如 Authorization 头)可能被带到域 B。凡是让用户可控输入进入 http 包装器并跟随外部重定向的路径都需要排查。
处置
升级至 9 月批次及以后版本;代码层面避免把敏感凭据用于会跟随任意重定向的请求。
哪些代码路径会中招
凡是使用 http:// 或 https:// 流包装器(file_get_contents、fopen、Guzzle 底层、部分 SDK 的文件下载)并且请求里带 Authorization / Cookie / Proxy-Authorization 头的场景,都可能在跨源重定向时把凭据转发出去。典型的危险组合是「用户可控 URL + 携带鉴权头」。
修复后的行为变化
修复后在跨主机、跨端口或 HTTPS→HTTP 降级时剥离这些敏感头。这属于行为变更:依赖「重定向后仍带鉴权头」的内部调用可能开始收到 401,升级后应对这类链路做回归验证,必要时改为显式二次请求。

修复补丁(官方提交)
该问题由 php-src 官方提交 5af9465ca890 修复(2026-09-14),提交说明为「Fix GHSA-fpwc-w8rq-cr92: strip credentials from user headers on cross-origin redirects」。改动涉及 3 个源码/测试文件,核心变更如下:
ext/standard/http_fopen_wrapper.c
@@ -81,27 +81,70 @@
 #define HTTP_WRAPPER_HEADER_INIT    1
 #define HTTP_WRAPPER_REDIRECTED     2
 #define HTTP_WRAPPER_KEEP_METHOD    4
+#define HTTP_WRAPPER_STRIP_AUTH     8

+static char *next_header_line(char *line)
+{
+	while (*line != '\0' && *line != '\r' && *line != '\n') {
+		line++;
+	}
+	if (*line == '\r') {
+		line++;
+	}
+	if (*line == '\n') {
+		line++;
+	}
+
+	return line;
+}
+
+/* Removes every line whose header name matches, along with the folded
+ * continuation lines carrying the rest of its value. Neither a repeated header
+ * nor an occurrence of the name inside another header's value may leave the real
+ * header behind, as that would defeat HTTP_WRAPPER_STRIP_AUTH. */
 static inline void strip_header(char *header_bag, char *lc_header_bag,
▲ 补丁片段摘自 php-src 官方仓库该提交
完整补丁与测试用例可在 php-src 仓库该提交页面查看:https://github.com/php/php-src/commit/5af9465ca890be679033d5fb0dc89b6ea071326b
▲ 官方公告页配图
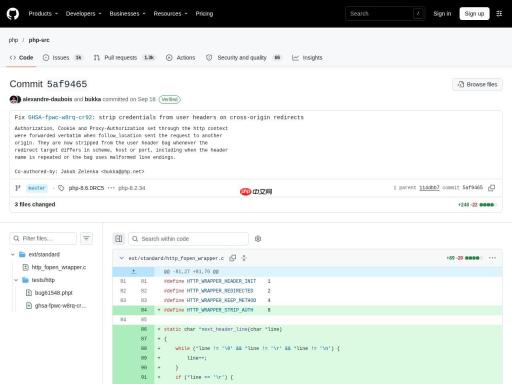
▲ 官方修复提交页面截图
关键信息
| 项目 | 内容 |
|---|---|
| 类目 | 安全漏洞 |
| 级别 | 中 |
| 日期 | 2026-09-24 |
| 关联编号 | CVE-2026-91766 / GHSA-fpwc-w8rq-cr92 |
| 影响范围 | 使用 HTTP 流包装器的应用 |
| 核验状态 | 已官方确认 |
| 修复提交 | 5af9465ca890(php-src) |
来源:https://github.com/php/php-src/security/advisories/GHSA-fpwc-w8rq-cr92





