






php-src 官方安全公告(2026-05-07,评级 high)披露 cve-2025-14179:pdo_firebird 驱动在准备 sql 语句时对引号字符串中的 nul 字节处理不当,查询的后续部分会被丢弃或错误拼接,可导致直接 sql 注入。修复版本为 8.2.31、8.3.31、8.4.21、8.5.6。
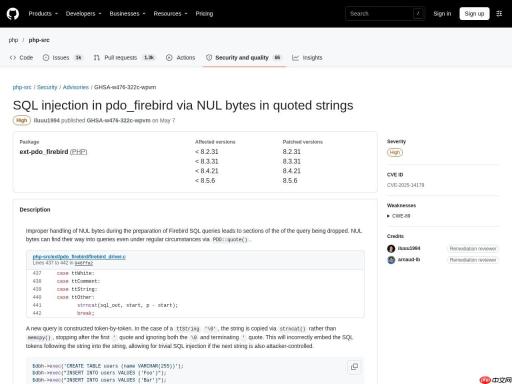
▲ php/php-src Security Advisories 公告页
漏洞机制
驱动逐段拼接预处理查询时,若参数是含 NUL 的字符串(经 PDO::quote() 也能产生),代码用 strncat() 而非 memcpy() 拷贝,复制在第一个引号处停止,NUL 与收尾引号都被忽略。于是字符串后面的 SQL 记号被错误地拼进字符串内部,查询语义整体改变。公告示例中,name = AND name = 'or 1=1--' 经预处理后变成 name = ' AND name = 'or 1=1--,注入条件直接生效并返回了全部用户数据。SELECT、INSERT 等语句类型均受影响。
影响与风险
使用 pdo_firebird 且把用户输入拼进查询(即便经过了 quote())的应用存在可被直接利用的 SQL 注入——攻击者可用 NUL 字节逃逸字符串边界,注入任意条件或语句。Firebird 在 PHP 生态中占比不高,但一旦命中就是高危:数据泄漏、越权读写均可行。
修复与升级
升级到 8.2.31 / 8.3.31 / 8.4.21 / 8.5.6 及以上。结构上更稳的做法是全程使用预处理参数绑定(bindValue),让驱动处理转义,避免手工 quote() 拼接;对已有 Firebird 应用做一次查询构造方式的审计。
修复补丁(官方提交)
该问题由官方提交 3f40b65323dd 修复(2026-05-03),提交说明为「GHSA-w476-322c-wpvm: [pdo_firebird] Fix SQL injection via NUL bytes in quoted strings」。改动涉及 2 个源码/测试文件,核心变更如下:

ext/pdo_firebird/firebird_driver.c
@@ -293,7 +293,7 @@ static FbTokenType getToken(const char** begin, const char* end)
 	return ret;
 }

-int preprocess(const zend_string* sql, char* sql_out, HashTable* named_params)
+int preprocess(const zend_string* sql, char* sql_out, size_t* sql_out_len, HashTable* named_params)
 {
 	bool passAsIs = 1, execBlock = 0;
 	zend_long pindex = -1;
@@ -324,7 +324,7 @@ int preprocess(const zend_string* sql, char* sql_out, HashTable* named_params)
 	if (l > 252) {
 		return 0;
 	}
-	strncpy(ident, i, l);
+	memcpy(ident, i, l);
 	ident[l] = '\0';
 	if (!strcasecmp(ident, "EXECUTE"))
 	{
@@ -349,7 +349,7 @@ int preprocess(const zend_string* sql, char* sql_out, HashTable* named_params)
 		if (l > 252) {
 			return 0;
 		}
-		strncpy(ident2, i2, l);
+		memcpy(ident2, i2, l);
 		ident2[l] = '\0';
 		execBlock = !strcasecmp(ident2, "BLOCK");
▲ 补丁片段摘自上述提交
完整补丁与测试用例可在官方提交页面查看:https://github.com/php/php-src/commit/3f40b65323dd1b85e9bab6878237d3867e449d5c
▲ 官方公告
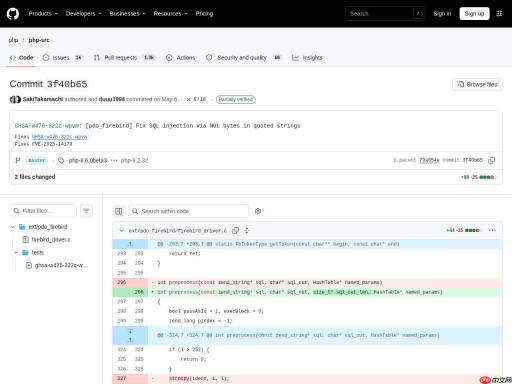
▲ php-src 修复提交
关键信息
| 项目 | 内容 |
|---|---|
| 类目 | 安全漏洞 |
| 级别 | 高 |
| 日期 | 2026-05-07 |
| 关联编号 | CVE-2025-14179 / GHSA-w476-322c-wpvm |
| 影响范围 | ext-pdo_firebird;官方修复版本 8.2.31 / 8.3.31 / 8.4.21 / 8.5.6 |
| 核验状态 | 已官方确认 |
| 受影响与修复 | ext-pdo_firebird 修复 8.2.31;ext-pdo_firebird 修复 8.3.31;ext-pdo_firebird 修复 8.4.21;ext-pdo_firebird 修复 8.5.6 |
| 修复提交 | 3f40b65323dd(PHP-8.2) |
来源:https://github.com/php/php-src/security/advisories/GHSA-w476-322c-wpvm


