






spring boot 全局异常处理捕获 oauth 回调异常,核心在于将 oauth 客户端库抛出的运行时异常(如 oauth2authenticationexception)映射到自定义的 @controlleradvice 中。具体做法是定义一个继承自 responseentityexceptionhandler 或仅使用 @restcontrolleradvice 的类,并在其中添加针对特定异常类型的 @exceptionhandler 方法。当 oauth 服务器返回错误响应或网络请求失败时,框架会自动触发这些处理器,从而允许你统一返回 json 错误或重定向到错误页面。
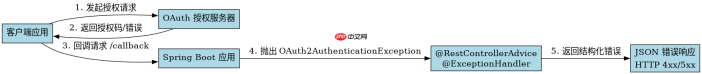
如何配置全局异常处理器以拦截 OAuth 异常
要拦截 OAuth 异常,需要创建一个配置类,使用 @RestControllerAdvice 注解。在这个类中,编写一个方法并使用 @ExceptionHandler(OAuth2AuthenticationException.class) 来指定处理的异常类型。该方法应返回一个 ResponseEntity,包含状态码和错误信息。这样,任何由 Spring Security OAuth2 或相关库抛出的认证异常都会被此方法捕获。
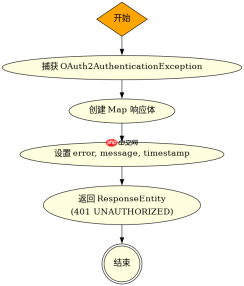
import org.springframework.http.HttpStatus; import org.springframework.http.ResponseEntity; import org.springframework.security.oauth2.core.OAuth2AuthenticationException; import org.springframework.web.bind.annotation.ExceptionHandler; import org.springframework.web.bind.annotation.RestControllerAdvice; import java.util.HashMap; import java.util.Map; @RestControllerAdvice public class GlobalOAuthExceptionHandler { @ExceptionHandler(OAuth2AuthenticationException.class) public ResponseEntity<map object>> handleOAuth2Exception(OAuth2AuthenticationException ex) { Map<string object> body = new HashMap(); body.put("error", "oauth_error"); body.put("message", ex.getMessage()); body.put("timestamp", System.currentTimeMillis()); return new ResponseEntity(body, HttpStatus.UNAUTHORIZED); } }</string></map>
上述代码定义了一个全局异常处理器。当 OAuth2AuthenticationException 发生时,它返回一个包含错误详情、消息和时间戳的 JSON 对象,HTTP 状态码为 401 Unauthorized。这确保了前端或调用方能接收到结构化的错误响应。
如何处理 OAuth 回调中的特定错误参数
在 OAuth 回调过程中,如果授权服务器返回错误参数(如 error=access_denied),Spring Security 通常会将其包装在 OAuth2AuthenticationException 中。为了更精细地处理这些错误,可以在异常处理器中提取 OAuth2Error 对象。通过检查错误的代码和描述,可以区分不同的失败原因,例如用户拒绝授权、客户端 ID 无效或重定向 URI 不匹配。

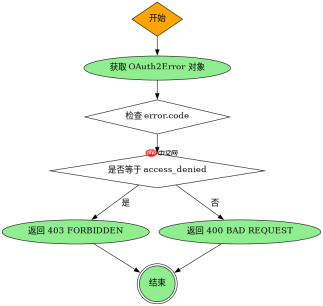
import org.springframework.http.HttpStatus; import org.springframework.http.ResponseEntity; import org.springframework.security.oauth2.core.OAuth2AuthenticationException; import org.springframework.security.oauth2.core.OAuth2Error; import org.springframework.web.bind.annotation.ExceptionHandler; import org.springframework.web.bind.annotation.RestControllerAdvice; import java.util.HashMap; import java.util.Map; @RestControllerAdvice public class DetailedOAuthExceptionHandler { @ExceptionHandler(OAuth2AuthenticationException.class) public ResponseEntity<map object>> handleDetailedOAuthException(OAuth2AuthenticationException ex) { OAuth2Error error = ex.getError(); Map<string object> body = new HashMap(); body.put("error_code", error.getCode()); body.put("error_description", error.getDescription()); body.put("original_exception", ex.getClass().getSimpleName()); if ("access_denied".equals(error.getCode())) { return new ResponseEntity(body, HttpStatus.FORBIDDEN); } return new ResponseEntity(body, HttpStatus.BAD_REQUEST); } }</string></map>
这段代码展示了如何从异常中提取具体的 OAuth 错误信息。如果错误代码是 access_denied,则返回 403 Forbidden;否则返回 400 Bad Request。这种处理方式允许后端根据具体的 OAuth 错误语义返回合适的 HTTP 状态码,便于前端进行针对性的 UI 提示或逻辑处理。
基于 OAuth 回调中 access_denied 错误的处理结果
当用户在 OAuth 授权页面上点击“拒绝”或发生其他导致 access_denied 的错误时,程序的实际结果是触发 DetailedOAuthExceptionHandler 中的逻辑。此时,系统会返回一个包含 error_code: access_denied 的 JSON 响应,且 HTTP 状态码为 403。开发者可以在前端监听这个状态码,并显示相应的提示信息,如“您已取消授权”,而不是通用的错误页面。这种机制确保了用户体验的一致性和错误信息的明确性。


