






PHP强制下载文件代码SESSION判断登录
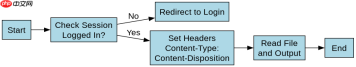
通过检查 $_session['logged_in'] 是否为真来验证用户登录状态,若未登录则重定向至登录页;若已登录,则设置正确的 content-type、content-disposition 等响应头,并使用 readfile() 输出文件内容以实现强制下载。
如何确保下载链接仅在登录后可见且安全?
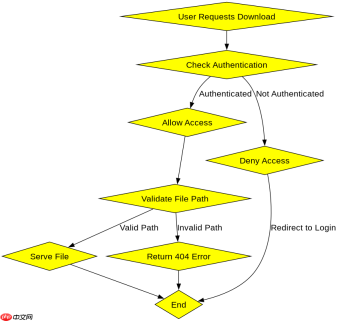
在提供下载链接的页面中,必须再次在服务端验证会话状态,防止直接访问下载脚本绕过前端限制。同时,应限制可下载的文件路径,避免路径遍历攻击。

A powerful memory management system powered by ReMe that provides persistent cross-session memory, automatic user preference application, and intelligent context compression for OpenClaw.
下载
由 ReMe 驱动的记忆管理系统,支持跨会话记忆持久化、自动应用用户偏好以及智能上下文压缩...
<?php session_start();
// 检查登录状态
if (!isset($_SESSION['user_id'])) {
    header('Location: login.php');
    exit;
}

$file = 'document.pdf';
$path = '/var/www/files/' . $file;

// 安全检查:防止路径遍历
if (basename($path) !== $file || !file_exists($path)) {
    http_response_code(404);
    echo 'File not found';
    exit;
}

header('Content-Description: File Transfer');
header('Content-Type: application/octet-stream');
header('Content-Disposition: attachment; filename="' . basename($path) . '"');
header('Expires: 0');
header('Cache-Control: must-revalidate');
header('Pragma: public');
header('Content-Length: ' . filesize($path));
readfile($path);
exit;
?>
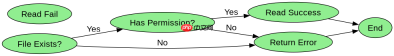
如果文件不存在或权限不足会怎样?
当请求的文件路径无效或服务器无权读取时,程序应返回404错误并终止执行,而不是抛出内部错误或泄露路径信息。这确保了系统的安全性和用户体验的一致性。
<?php // 模拟文件不存在的情况
$file = 'nonexistent.pdf';
$path = '/var/www/files/' . $file;

if (!file_exists($path)) {
    http_response_code(404);
    echo 'File not found';
    exit;
}

// 如果存在,继续下载逻辑
header('Content-Type: application/octet-stream');
header('Content-Disposition: attachment; filename="' . basename($path) . '"');
readfile($path);
?>
php免费学习视频:立即使用
踏上前端学习之旅,开启通往精通之路!从前端基础到项目实战,循序渐进,一步一个脚印,迈向巅峰!





